I'm Jada, founder of The SaaSCE Boutique and host of Let's Talk IRM.
I teach integrated risk management the way it works in practice.
CISSP · CIS-IRM · ServiceNow CSA · M.S. Cybersecurity · 10+ years in GRC and IRM
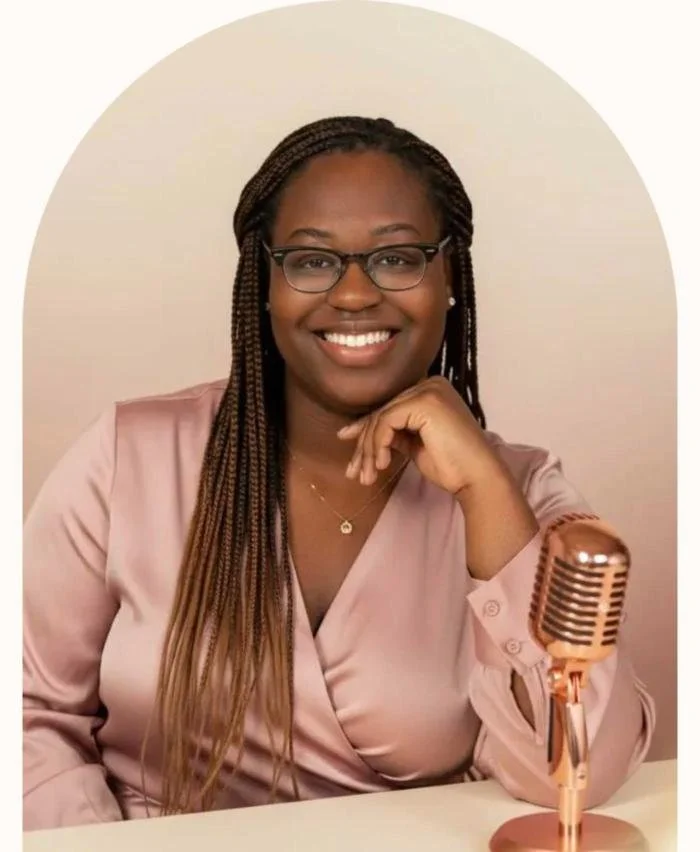
What I've built and led
EXPERIENCE
My background
10+ years in GRC and IRM, from government contracting under CMMC, NIST 800-171 and DFARS to ServiceNow IRM programs. CISSP, CIS-IRM, ServiceNow CSA, and a master's in cybersecurity.
FOCUS AREAS
Where I work
ServiceNow IRM: Core IRM, and Continuous Authorization and Monitoring (CAM).
Frameworks: CMMC, NIST 800-171, NIST 800-172, DFARS.
THE SHOW
Let's Talk IRM
A podcast for GRC practitioners and ServiceNow IRM teams, moderated by Meesh.
Selected work: exception management in ServiceNow IRM
The problem: the exception process had become a catch-all for requests that didn't fit any other form, and device exceptions were hard to track, including when they expired or were due for review.
What I did: separated true risk exceptions from access requests, with a triage path for anything that didn't fit. Tied each device exception to its record in the CMDB, and split the roles: security recommends, IT approves the technical change, and the business owner accepts the risk. Expirations never reset, owners re-approve extensions, and exceptions are flagged for removal when someone leaves the approved business unit.
Agile process for a distributed ServiceNow IRM team
The problem: there was no agile process, and customization requests came in from several teams without any vetting.
What I did: set up one intake path and one ranked backlog with a single prioritization owner. Made out-of-the-box first the rule, so customizations need a business case and approval before they reach a sprint. Added a story template with testable acceptance criteria, capacity-based planning, peer testing and UAT, and rolled it out in phases so the team wasn't overwhelmed.
Also on the show: the IRM Foundations demo series, hands-on walkthroughs of Authority Documents, Citations and Control Objectives in a live ServiceNow instance.
Why The SaaSCE Boutique exists
I started teaching because I kept seeing organizations try to put an IRM strategy in place with incorrect information, or none at all. Good IRM guidance is hard to find, and most of what's out there starts with the tool. This is where I share what actually works, from one practitioner to another.
“Jada approaches complex risk and control topics with strong analytical rigor, clear documentation, and a structured scripting mindset that makes her work easy to understand and operationalize. She reliably translates requirements into well-organized processes and testing approaches, then uses results to drive tangible improvements rather than simply checking a box.”
— A GRC leader who managed Jada directly
Reach out if you'd like to chat or collaborate on something.